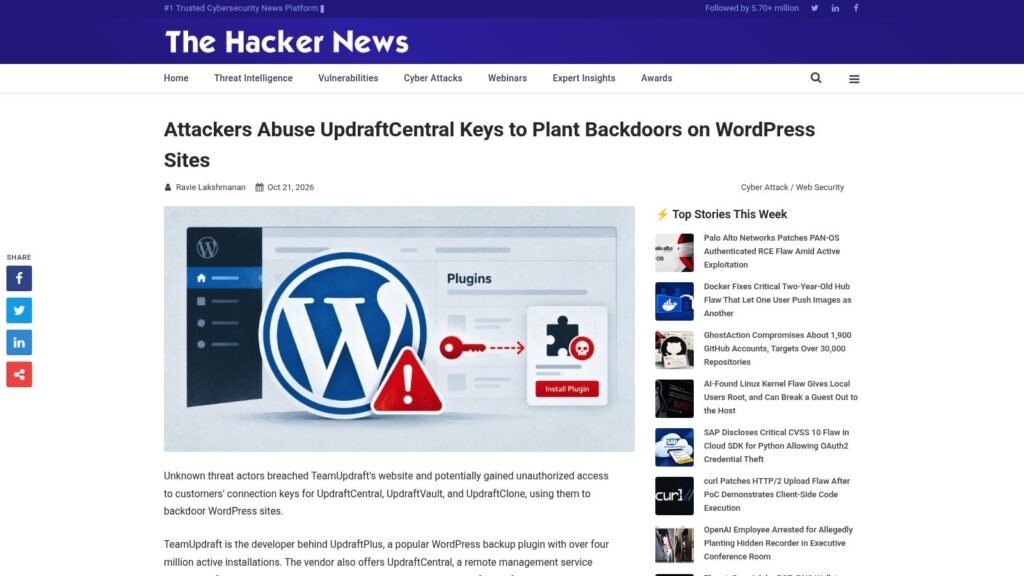
Attackers exploited unauthorized access to TeamUpdraft’s website to steal connection keys for UpdraftCentral, UpdraftVault, and UpdraftClone, enabling them to install backdoor plugins on thousands of WordPress sites managed remotely via UpdraftCentral. TeamUpdraft responded by resetting keys, releasing plugin updates to revoke compromised connections, and advising users to revoke access and check for unauthorized admin accounts. Security researchers confirmed the attackers used valid UpdraftCentral keys to execute commands creating persistent backdoor admin accounts, highlighting the critical risk to WordPress site security through compromised remote management credentials.
https://thehackernews.com/2026/10/attackers-abuse-updraftcentral-keys-to.html