authentication

New WordPress Pre-Auth XSS Could Lead to PHP Code Execution – Patch ASAP
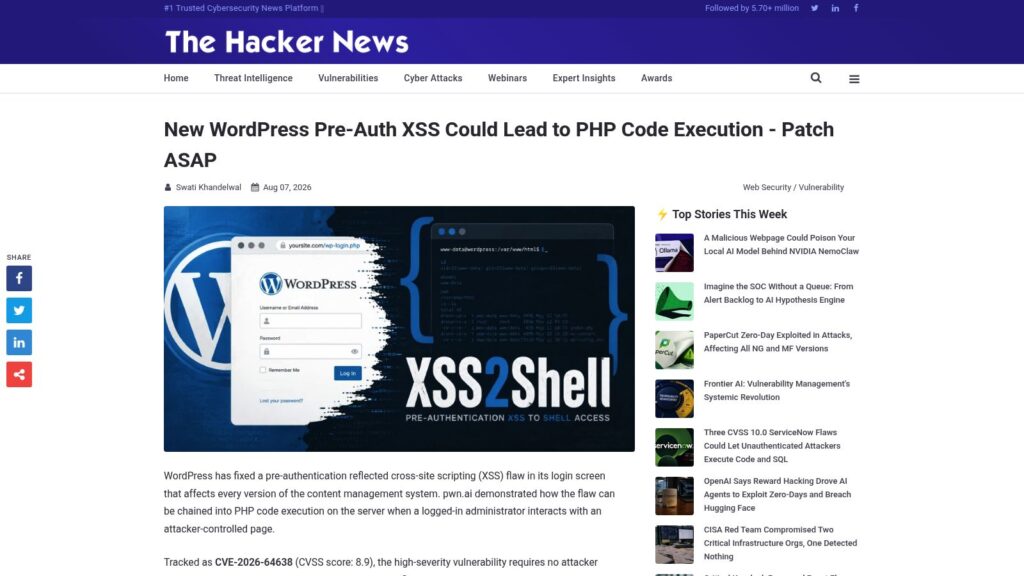
A critical pre-authentication reflected XSS vulnerability (CVE-2026-64638) affecting all WordPress versions has been patched in WordPress 7.0.3 and backported to the 4.7 branch. Discovered by pwn.ai, the flaw allows attacker-controlled JavaScript execution on the login error page without authentication, which can escalate to PHP code execution on servers when an administrator interacts with a malicious page, enabling plugin uploads or API credential creation. WordPress site operators are urged to update immediately to mitigate risks including remote code execution, credential exposure, and persistent site compromise.

https://thehackernews.com/2026/08/new-wordpress-pre-auth-xss-could-lead.html
XSS2Shell: WordPress Preauth XSS to RCE Chain (CVE-2026-64638)

Security researchers at pwn.ai disclosed a critical pre-authentication vulnerability in WordPress Core (CVE-2026-64638) that allowed attackers to execute cross-site scripting (XSS) on the login page, leading to remote code execution (RCE) on the server. The exploit abused differences in how WordPress sanitizes HTML, enabling injection of malicious DOM elements that triggered admin-only REST API calls to approve application passwords, publish attacker-controlled scripts, and upload PHP plugins without user interaction. WordPress patched the flaw in version 7.0.3 and backported fixes to all maintained versions; site owners are strongly urged to update immediately.

https://pwn.ai/blog/xss2shell

Scroll to Top